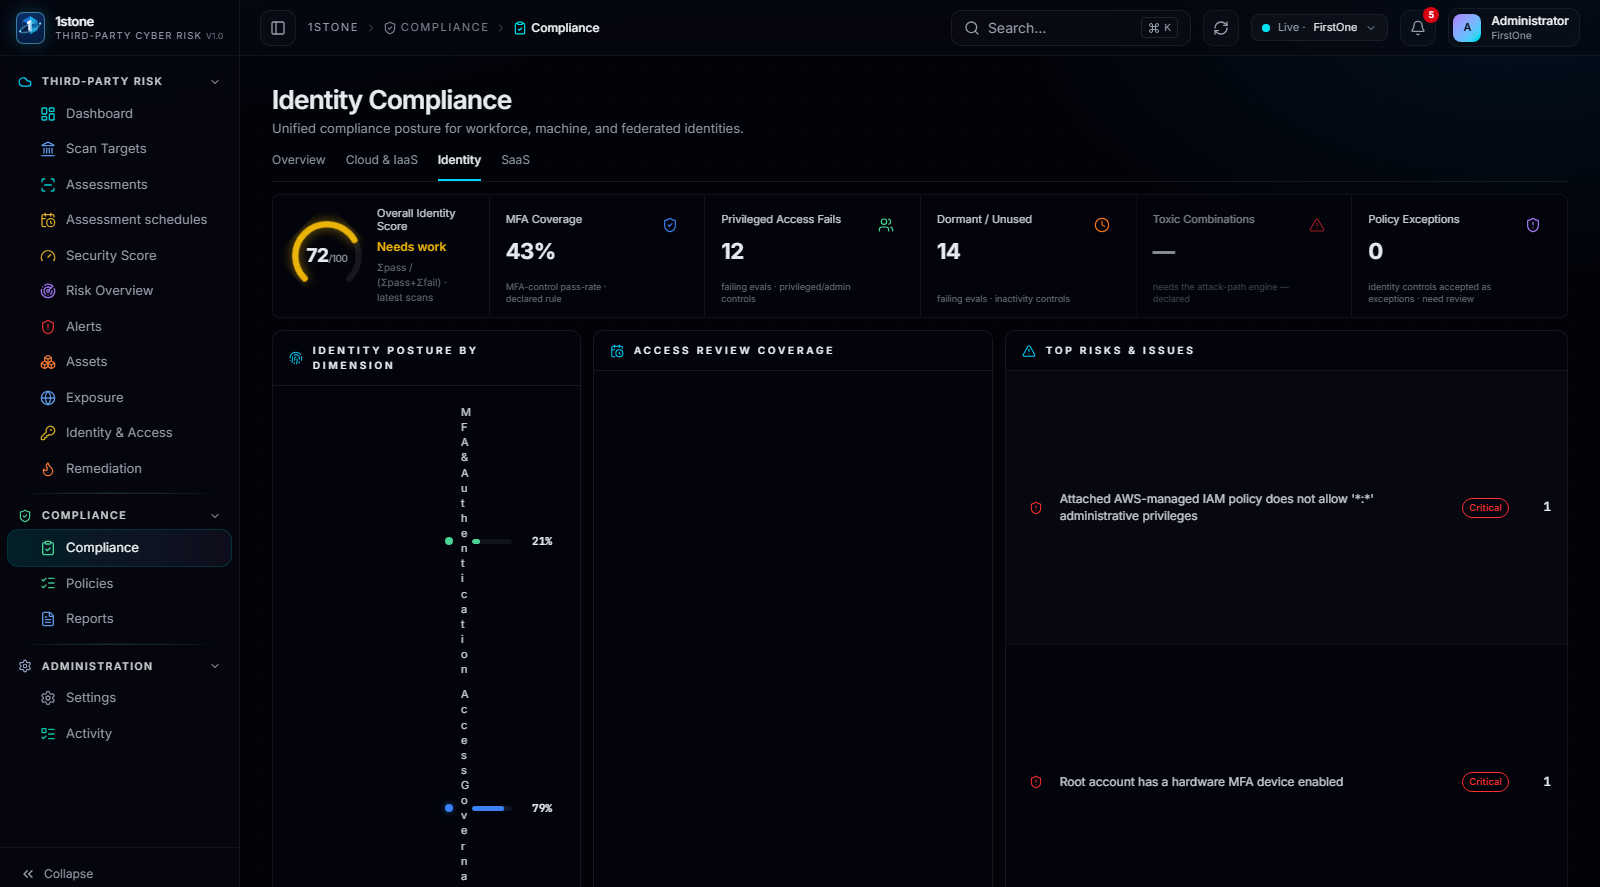
One evidence base, many mappings
Every control evaluated on a connected account is mapped to the frameworks it satisfies. A single misconfigured storage policy can show up as a failed control under more than one framework at once, because it is the same evidence, mapped more than one way — not nine separate collection exercises.
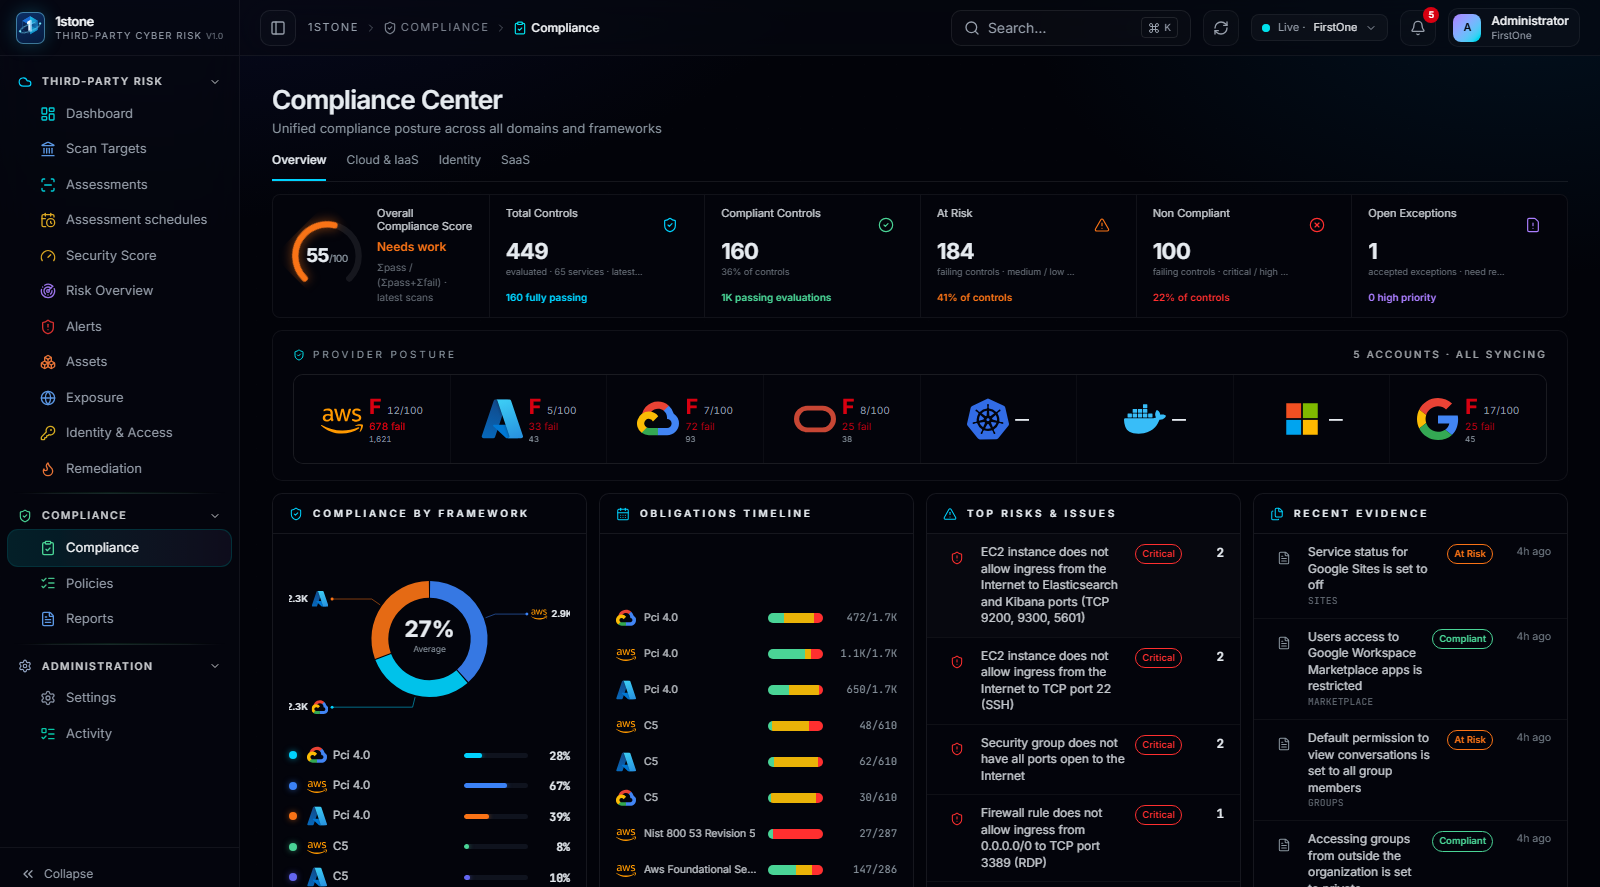
Coverage by environment
Because the same Cloud, Identity and SaaS environments feed the Security Score, they also feed framework coverage — a reviewer can see PCI DSS 4.0 or ISO 27001 status specifically for the cloud environment, or for identity, or for the SaaS estate.
- Frameworks evaluated: CIS, NIST 800-53, PCI DSS 4.0, ISO 27001, GDPR, DORA, FedRAMP, GxP, C5
- Coverage broken down by Cloud, Identity and SaaS
- No self-attestation step in the evaluation
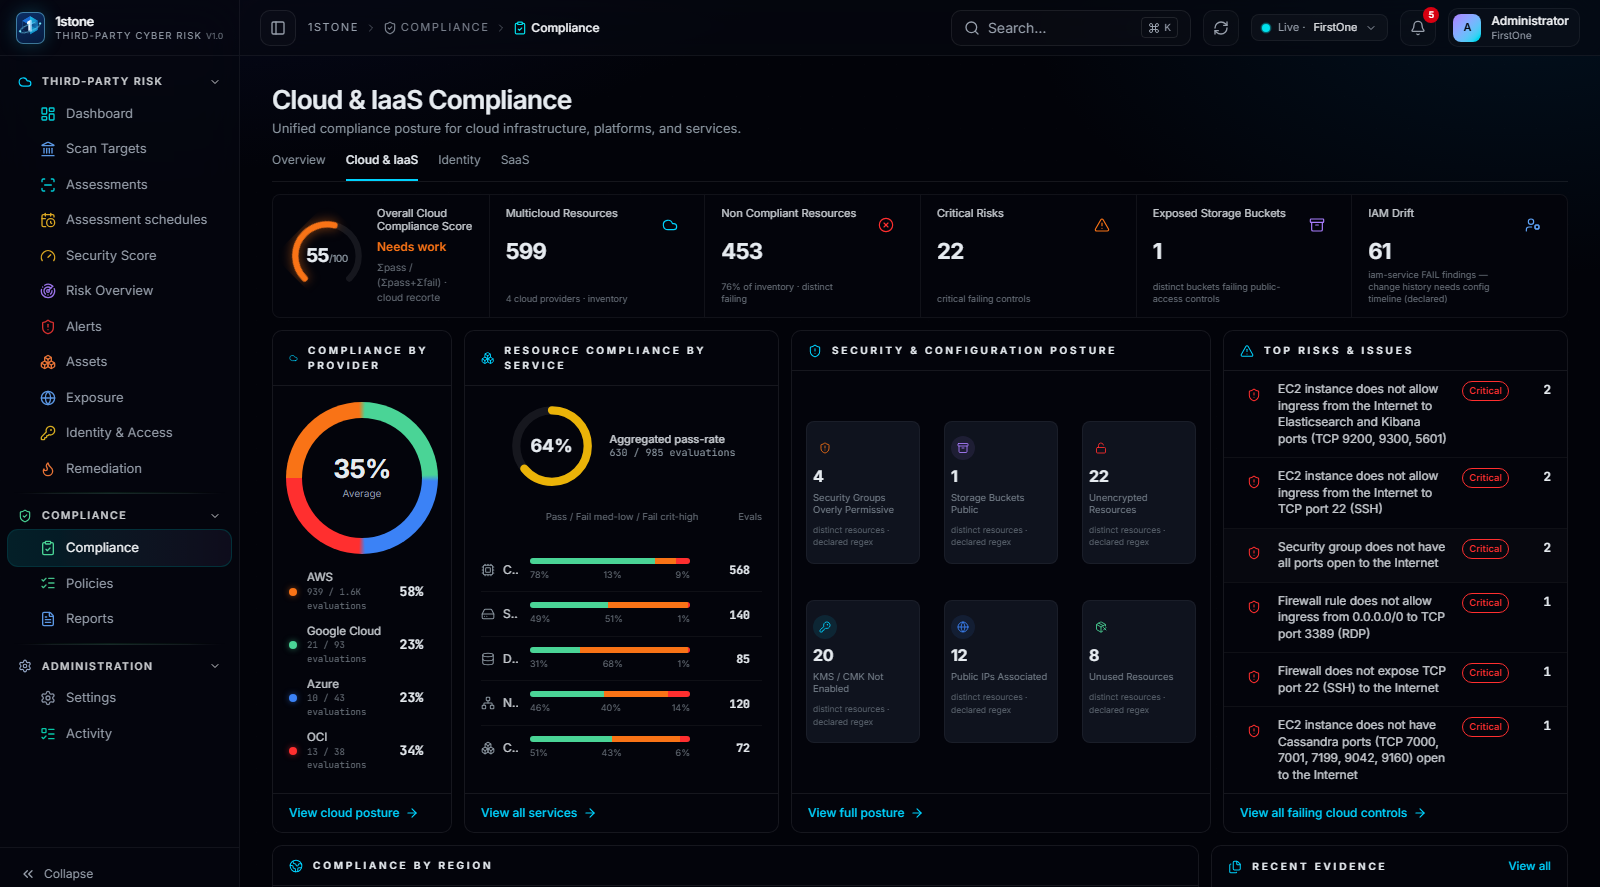
Identity and SaaS coverage
The same per-framework view is available scoped to identity findings and to the SaaS estate, so a gap in Microsoft 365 configuration or in access hygiene is traceable to the exact framework clause it affects.