Exposure

Exposure, read from the inside: public resources, open ports and the regions involved

Exposure here is not inferred by scanning the internet for the third party's assets — it is read directly from the connected accounts: which resources are public, which ports are open, and where they live.

Blog

August 13, 2026 · 9 min read

01

Signals sourced from the account, not from a perimeter scan

Because the platform reads the third party's own account configuration, exposure signals such as a public storage resource, an open management port or an unrestricted security group are exact — they come from the resource's own policy, not from an inference made outside the network.
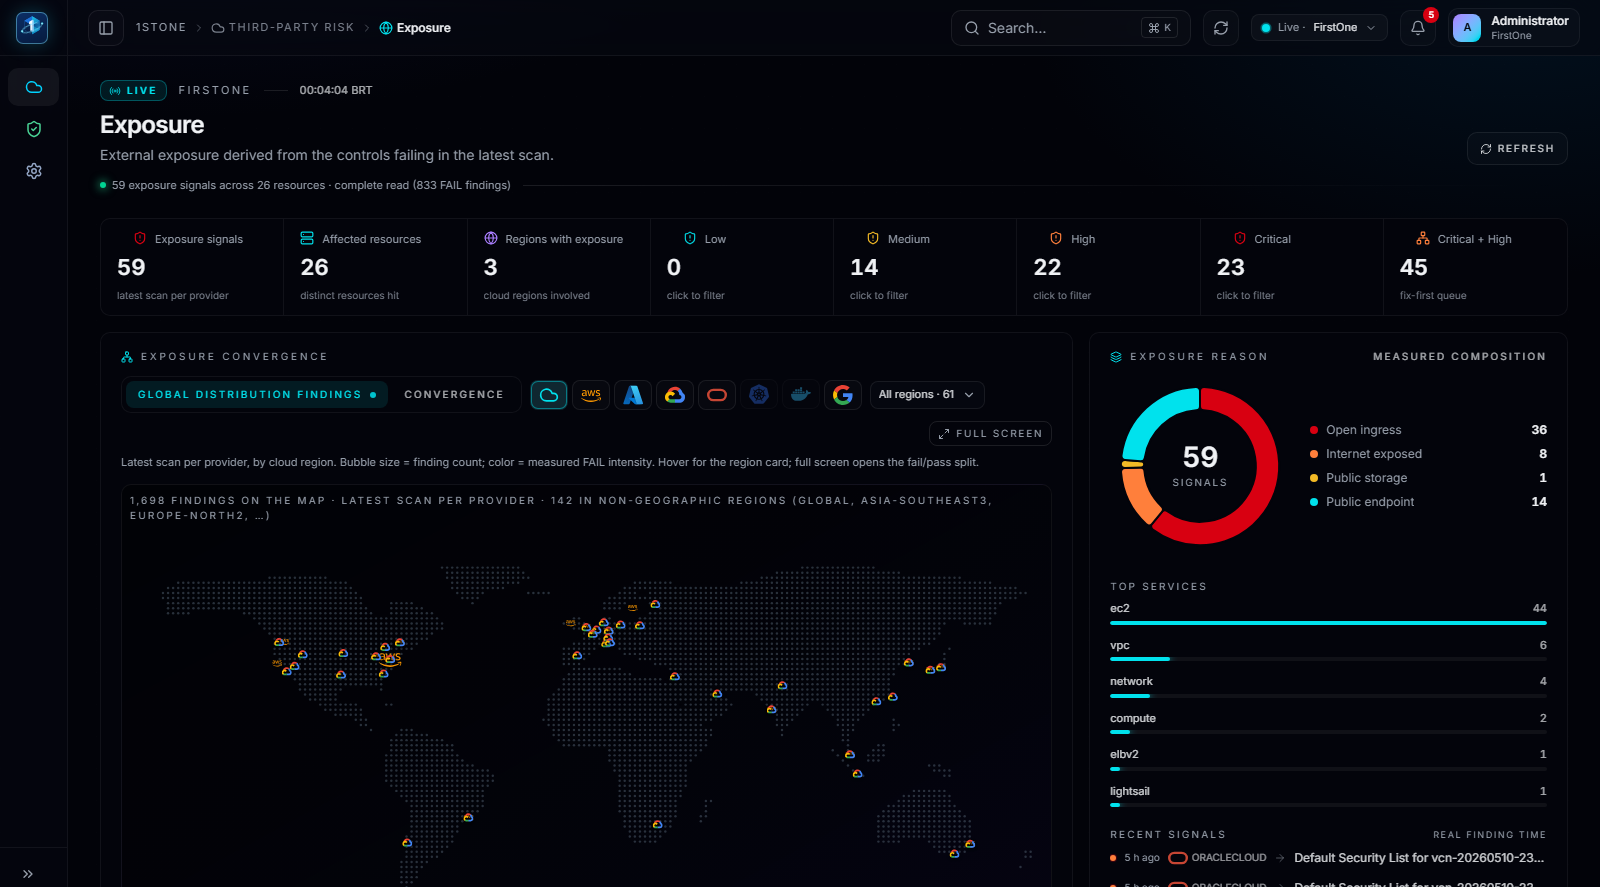
Exposure: public resources, open ports and regions involved, with severity per signal.
02

Where exposure concentrates

A convergence map crosses exposure signals with severity and with the connected environment they belong to, so a reviewer can see quickly whether exposure concentrates in one account, one region or one provider.

  • Public resources flagged with the policy that made them public
  • Open ports and the service behind them
  • Regions involved, to localize where exposure concentrates
1stone Research

Talk to the team about a third-party program

A working session against your actual third-party portfolio: how workspaces are created, which accounts get connected first, and what the Security Score looks like in week one.

Request a walkthrough