Reporting

The report a committee actually reads: score, open alerts and remediation progress

A risk committee does not need raw findings. It needs the score, what changed since the last review, and whether remediation is moving in the right direction — in a document that is ready to print, not a dashboard someone has to interpret live.

Blog

July 28, 2026 · 8 min read

01

What the report contains

The report package pulls together the third party's Security Score and A–F grade, the count and severity of open alerts, and the state of open and resolved remediation cases, into a document a committee can read without opening the console.
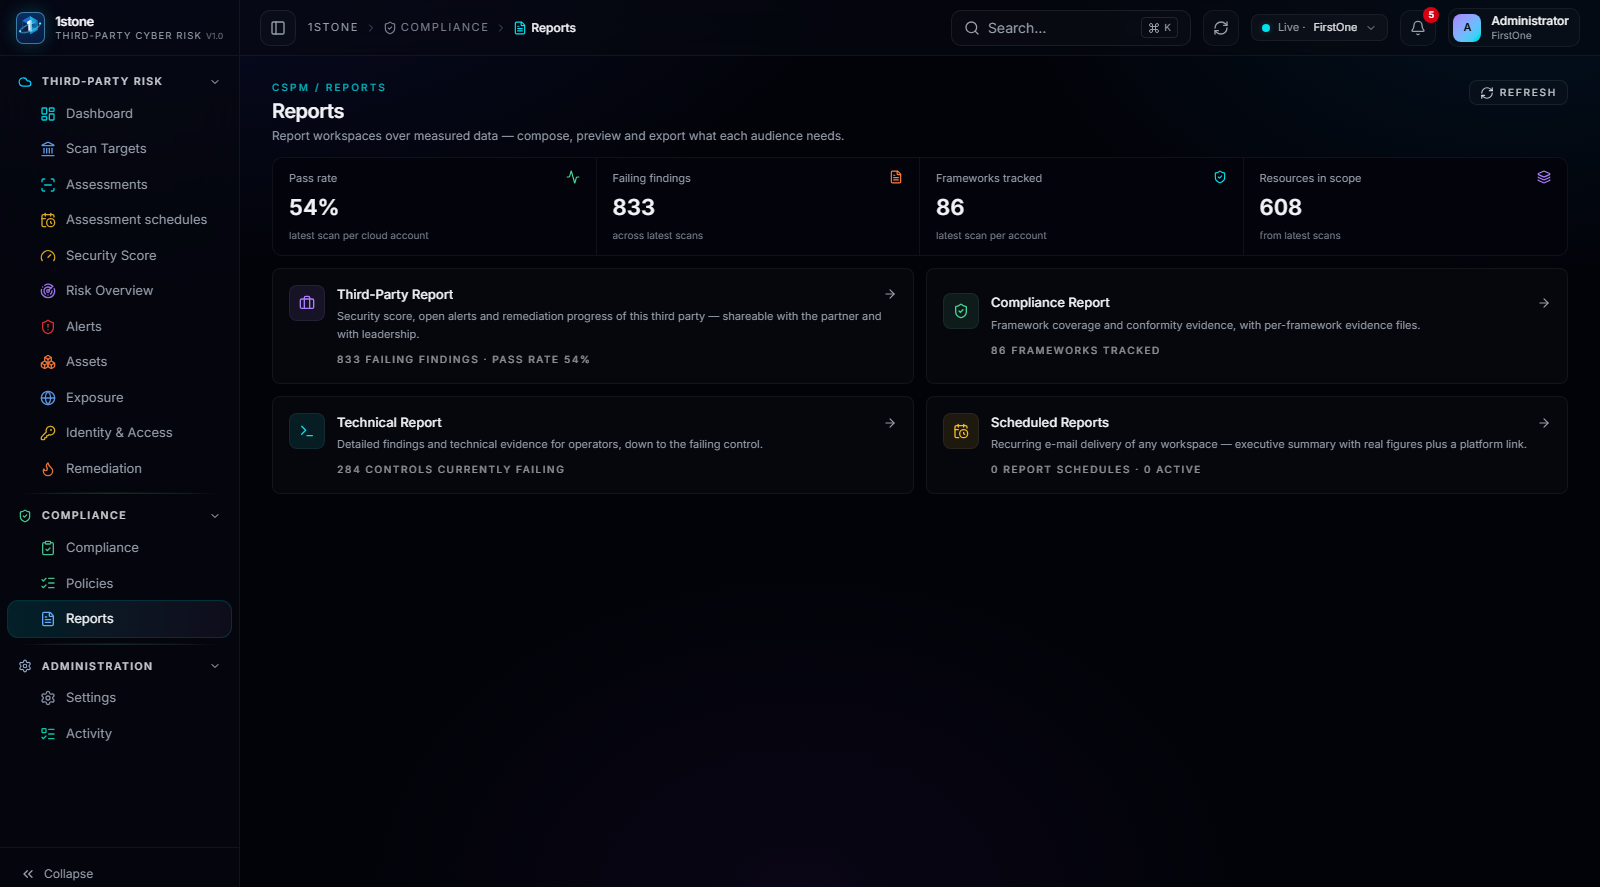
Reports: the committee-ready report with Security Score, open alerts and remediation progress.
02

Two reports, two audiences

The same underlying evidence produces two different reports: one built for the third party's own team, focused on what to fix next, and one built for the contracting organization's risk committee, focused on trend and exposure across the relationship.

  • Third-party report: what to fix next, ranked
  • Committee report: score trend, open alerts and remediation progress
  • Both generated from the same evidence, ready to export
1stone Research

Talk to the team about a third-party program

A working session against your actual third-party portfolio: how workspaces are created, which accounts get connected first, and what the Security Score looks like in week one.

Request a walkthrough